1 Purpose of the API
Read conference data out — never write through the API.
Effective Date: 11-07-2026
The API is designed to allow authorized users to programmatically retrieve conference details, paper metadata, and submission statuses for integration into external applications, websites, or internal systems.
The API provides read-only access to data that conference organizers have chosen to make available through the platform.
The API does not provide functionality for modifying, submitting, or deleting data; all write operations must be performed through the main platform interface.
2 Authentication and Access
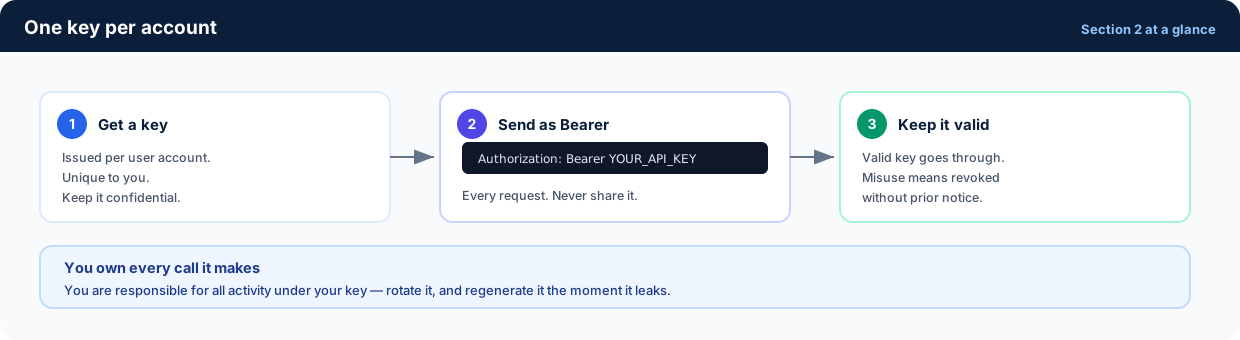
One key per account, sent as a Bearer token, kept confidential.
Access to the API requires a valid API Key, which is issued to registered users through the platform's API management interface.
Each API request must include the API Key in the Authorization header using the Bearer scheme:
Authorization: Bearer YOUR_API_KEY
API Keys are unique to each user account and must be kept confidential. Sharing API Keys with unauthorized parties is strictly prohibited.
The platform reserves the right to revoke or invalidate any API Key at any time without prior notice if misuse is detected.
Header, not URL. Always send the key in the Authorization header — never in query strings, logs, or client-side code.
3 Permitted Use
Four things you may build with the API.
You are permitted to use the API solely for the following purposes:
- Displaying conference and paper information on your own website or application.
- Integrating conference data with your internal tools or third-party services.
- Creating analytics or reporting based on the retrieved data.
- Enhancing user experience by providing real-time conference updates.
All usage must be in compliance with applicable laws and regulations, including data protection and privacy laws.
4 Prohibited Use
Seven lines you must not cross.
You may not use the API for any of the following activities:
- Redistributing, reselling, or sublicensing the API or its data.
- Storing or caching large volumes of data for purposes other than immediate display to end users.
- Using the API to build a competing product or service.
- Attempting to bypass rate limits or security measures.
- Scraping or data mining beyond the intended usage patterns.
- Using the API for any unlawful, fraudulent, or harmful activities.
- Impersonating another user or accessing data that you are not authorized to view.
Violation of these prohibitions may result in immediate suspension or termination of API access.
Immediate cut-off. Prohibited use — scraping, reselling, competing clones, limit bypassing — can end your access without warning.
5 Rate Limits and Throttling
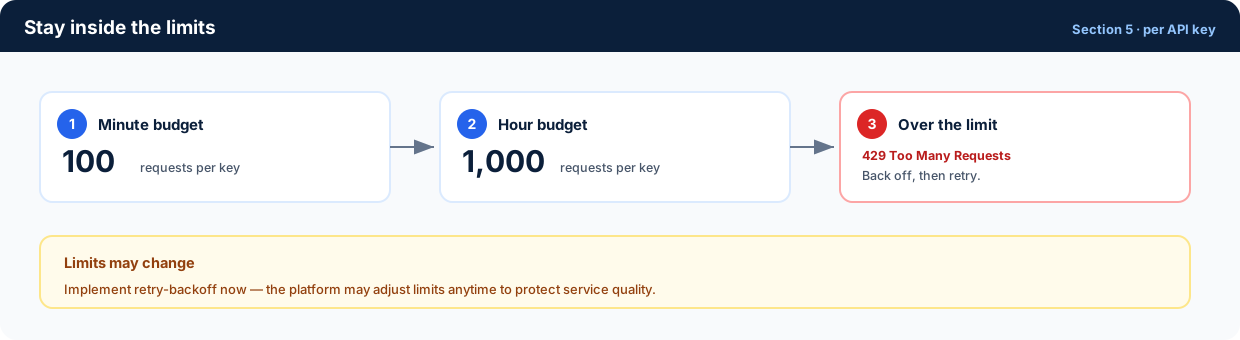
100 per minute, 1,000 per hour — then 429.
To ensure fair usage and system stability, the API enforces rate limits.
The current limits are:
- 100 requests per minute per API Key.
- 1,000 requests per hour per API Key.
If you exceed these limits, the API will respond with HTTP status code 429 Too Many Requests and may temporarily block further requests.
You are expected to implement appropriate retry-backoff mechanisms in your application to handle rate-limit responses.
The platform reserves the right to adjust these limits at any time to maintain service quality.
Back off on 429. Treat 429 as "slow down", not "retry instantly" — hammering a throttled endpoint only extends the block.
6 Data Ownership and Intellectual Property
The data belongs to organizers and authors — not to API consumers.
The API provides access to data that is owned by conference organizers and authors. The platform does not claim ownership of any data retrieved via the API.
You are granted a non-exclusive, non-transferable license to access and use the data solely for the purposes described in Section 3 (Permitted Use).
You must respect the intellectual property rights of the data owners and may not remove, obscure, or alter any copyright, trademark, or other proprietary notices.
By using the API, you acknowledge that the platform does not endorse, verify, or guarantee the accuracy or completeness of the data provided through the API.
7 Data Accuracy and Disclaimer
Provided "as is" — verify before you rely on it.
The platform makes reasonable efforts to ensure the accuracy of data provided through the API but does not warrant that the data is error-free, complete, or up-to-date.
The data is provided "as is" and "as available" without any warranties of any kind, either express or implied.
You are responsible for verifying the accuracy of any data you retrieve and for any decisions or actions you take based on that data.
The platform shall not be liable for any errors, omissions, or inaccuracies in the data or for any loss or damage resulting from reliance on the data.
8 Security Requirements
Protect the key and everything it unlocks.
You must implement appropriate security measures to protect your API Key and any data obtained through the API.
Recommended practices include:
- Storing API Keys in environment variables or secure vaults, not in source code.
- Rotating API Keys periodically.
- Using HTTPS exclusively for all API requests.
- Restricting API Key usage to known IP addresses where possible.
- Immediately revoking and regenerating keys if they are compromised.
You must also ensure that your applications do not expose API Keys to end users or third parties.
9 Privacy and Confidentiality
Personal data in responses stays protected.
Any data retrieved through the API may include personal information such as author names, email addresses, or affiliations. You must handle such data in compliance with applicable privacy laws (e.g., GDPR, CCPA).
You are prohibited from using the API to harvest personal information for purposes other than those explicitly permitted by the data owner.
You must maintain the confidentiality of any non-public information obtained through the API and may not disclose it to unauthorized parties.
10 Limitation of Liability
You build on the API at your own risk.
The platform provides the API as a service to facilitate data access. The platform shall not be liable for:
- Any direct, indirect, incidental, special, or consequential damages arising from the use or inability to use the API.
- Loss of data, revenue, or business opportunities.
- Third-party claims arising from your use of the API.
- Any disruptions, errors, or service interruptions caused by factors beyond the platform's reasonable control.
You assume all responsibility for your use of the API and any consequences thereof.
11 API Key Management
Your key, your responsibility — even for uses you did not authorize.
API Keys are issued to individual user accounts and are associated with the privileges of that account.
You are responsible for all activities performed using your API Key, even if those activities were not authorized by you.
If you suspect that your API Key has been compromised, you must immediately disable it through the API management interface and generate a new key.
The platform may revoke API Keys that are inactive for an extended period or that are used in a manner inconsistent with this Policy.
12 Termination and Suspension
Access can end — with or without cause or notice.
The platform reserves the right to suspend or terminate your access to the API at any time, with or without cause, and with or without notice.
Grounds for suspension or termination include, but are not limited to:
- Violation of this Policy or any other applicable terms.
- Excessive usage that degrades service for other users.
- Engaging in unlawful or harmful activities.
- Failure to pay applicable fees (if any).
Upon termination, you must cease all use of the API and delete any stored data obtained through the API.
Clean exit required. Terminated means terminated — stop calling the API and delete stored API data.
13 Changes to this Policy
Updates take effect upon posting.
The platform may update this Policy from time to time to reflect changes in technology, legal requirements, or operational needs.
Any changes will be effective immediately upon posting the updated Policy on this page.
Your continued use of the API after any such changes constitutes your acceptance of the revised Policy.
We encourage you to review this Policy periodically to stay informed of any updates.
14 Contact Information
Questions about this Policy? Talk to us.
If you have any questions, concerns, or feedback regarding this API Policy, please contact us:
- Censula Support Team
- Email: support@censula.com
- Website: censula.com
Building an integration? Read the API developer portal first — most technical questions are answered there with runnable examples.